
Skip to content
AI NEWS JOURNAL
AI, IN PERSPECTIVE

Search AI news

Search headlines, summaries and articles to connect the dots.

Newest first

Microsoft open-sources Agensh: a decentralized framework that supports 1024 autonomous, collaboratively operating AI coding agents.

On October 25, 2026, Microsoft Research open-sourced Agensh, a multi-agent runtime framework that operates without a central coordinator, enabling 1 to 1,024 LLM-powered coding agents to self-organize and collaborate on ProgramBench. The system achieves decentralized coordination through shared dashboards inspired by Gitea, Mattermost, and DeLM, with all agents following the same prompt-driven five-step loop; its scalability has been validated in a Linux + Docker environment.
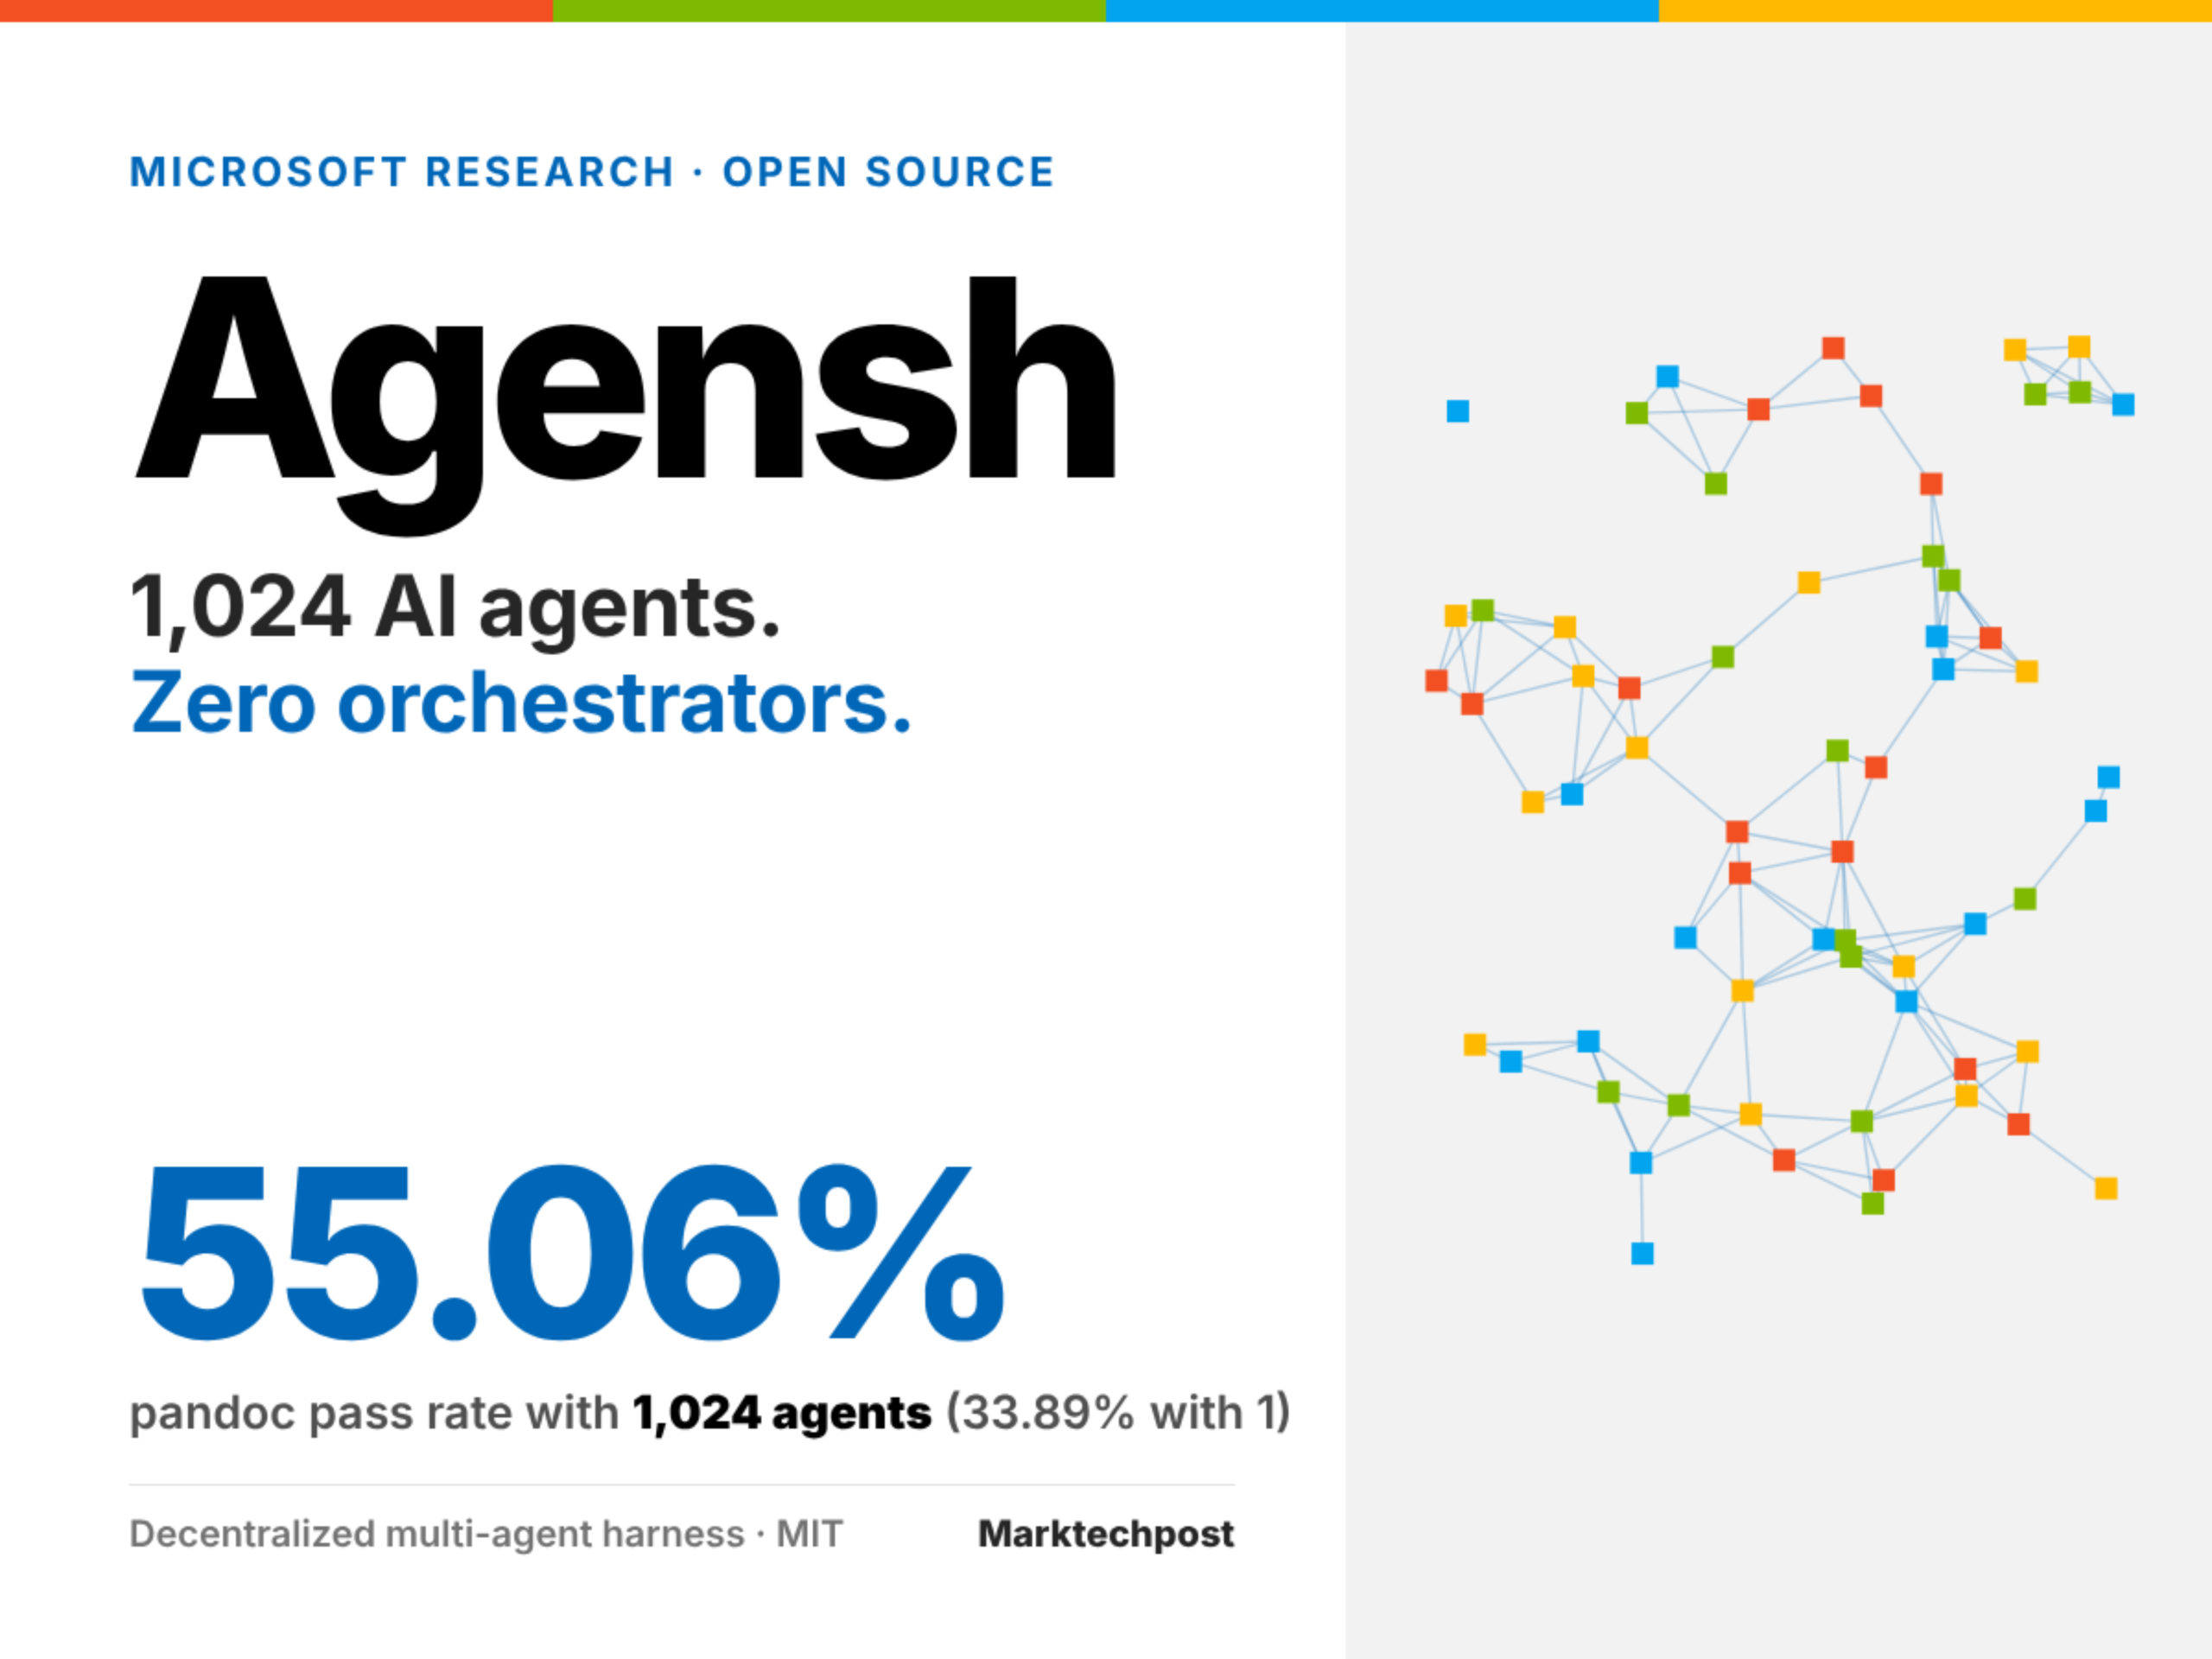
Microsoft Open-Sources Agensh: A Multi-Agent Harness for 1,024 Agents

Why it matters:This achievement represents a significant evolution in multi-agent system architectures—abandoning the traditional “master‑agent” paradigm and enabling large‑scale self‑organization through prompt engineering and lightweight service composition. Empirical results on ProgramBench (e.g., 128 agents achieving a 49% improvement in task load balancing across five tasks) establish a new benchmark for distributed AI engineering. Released under the MIT License and compatible with mainstream single‑agent tools such as Copilot CLI, it offers valuable guidance for practical development.
Timeline and related coverage

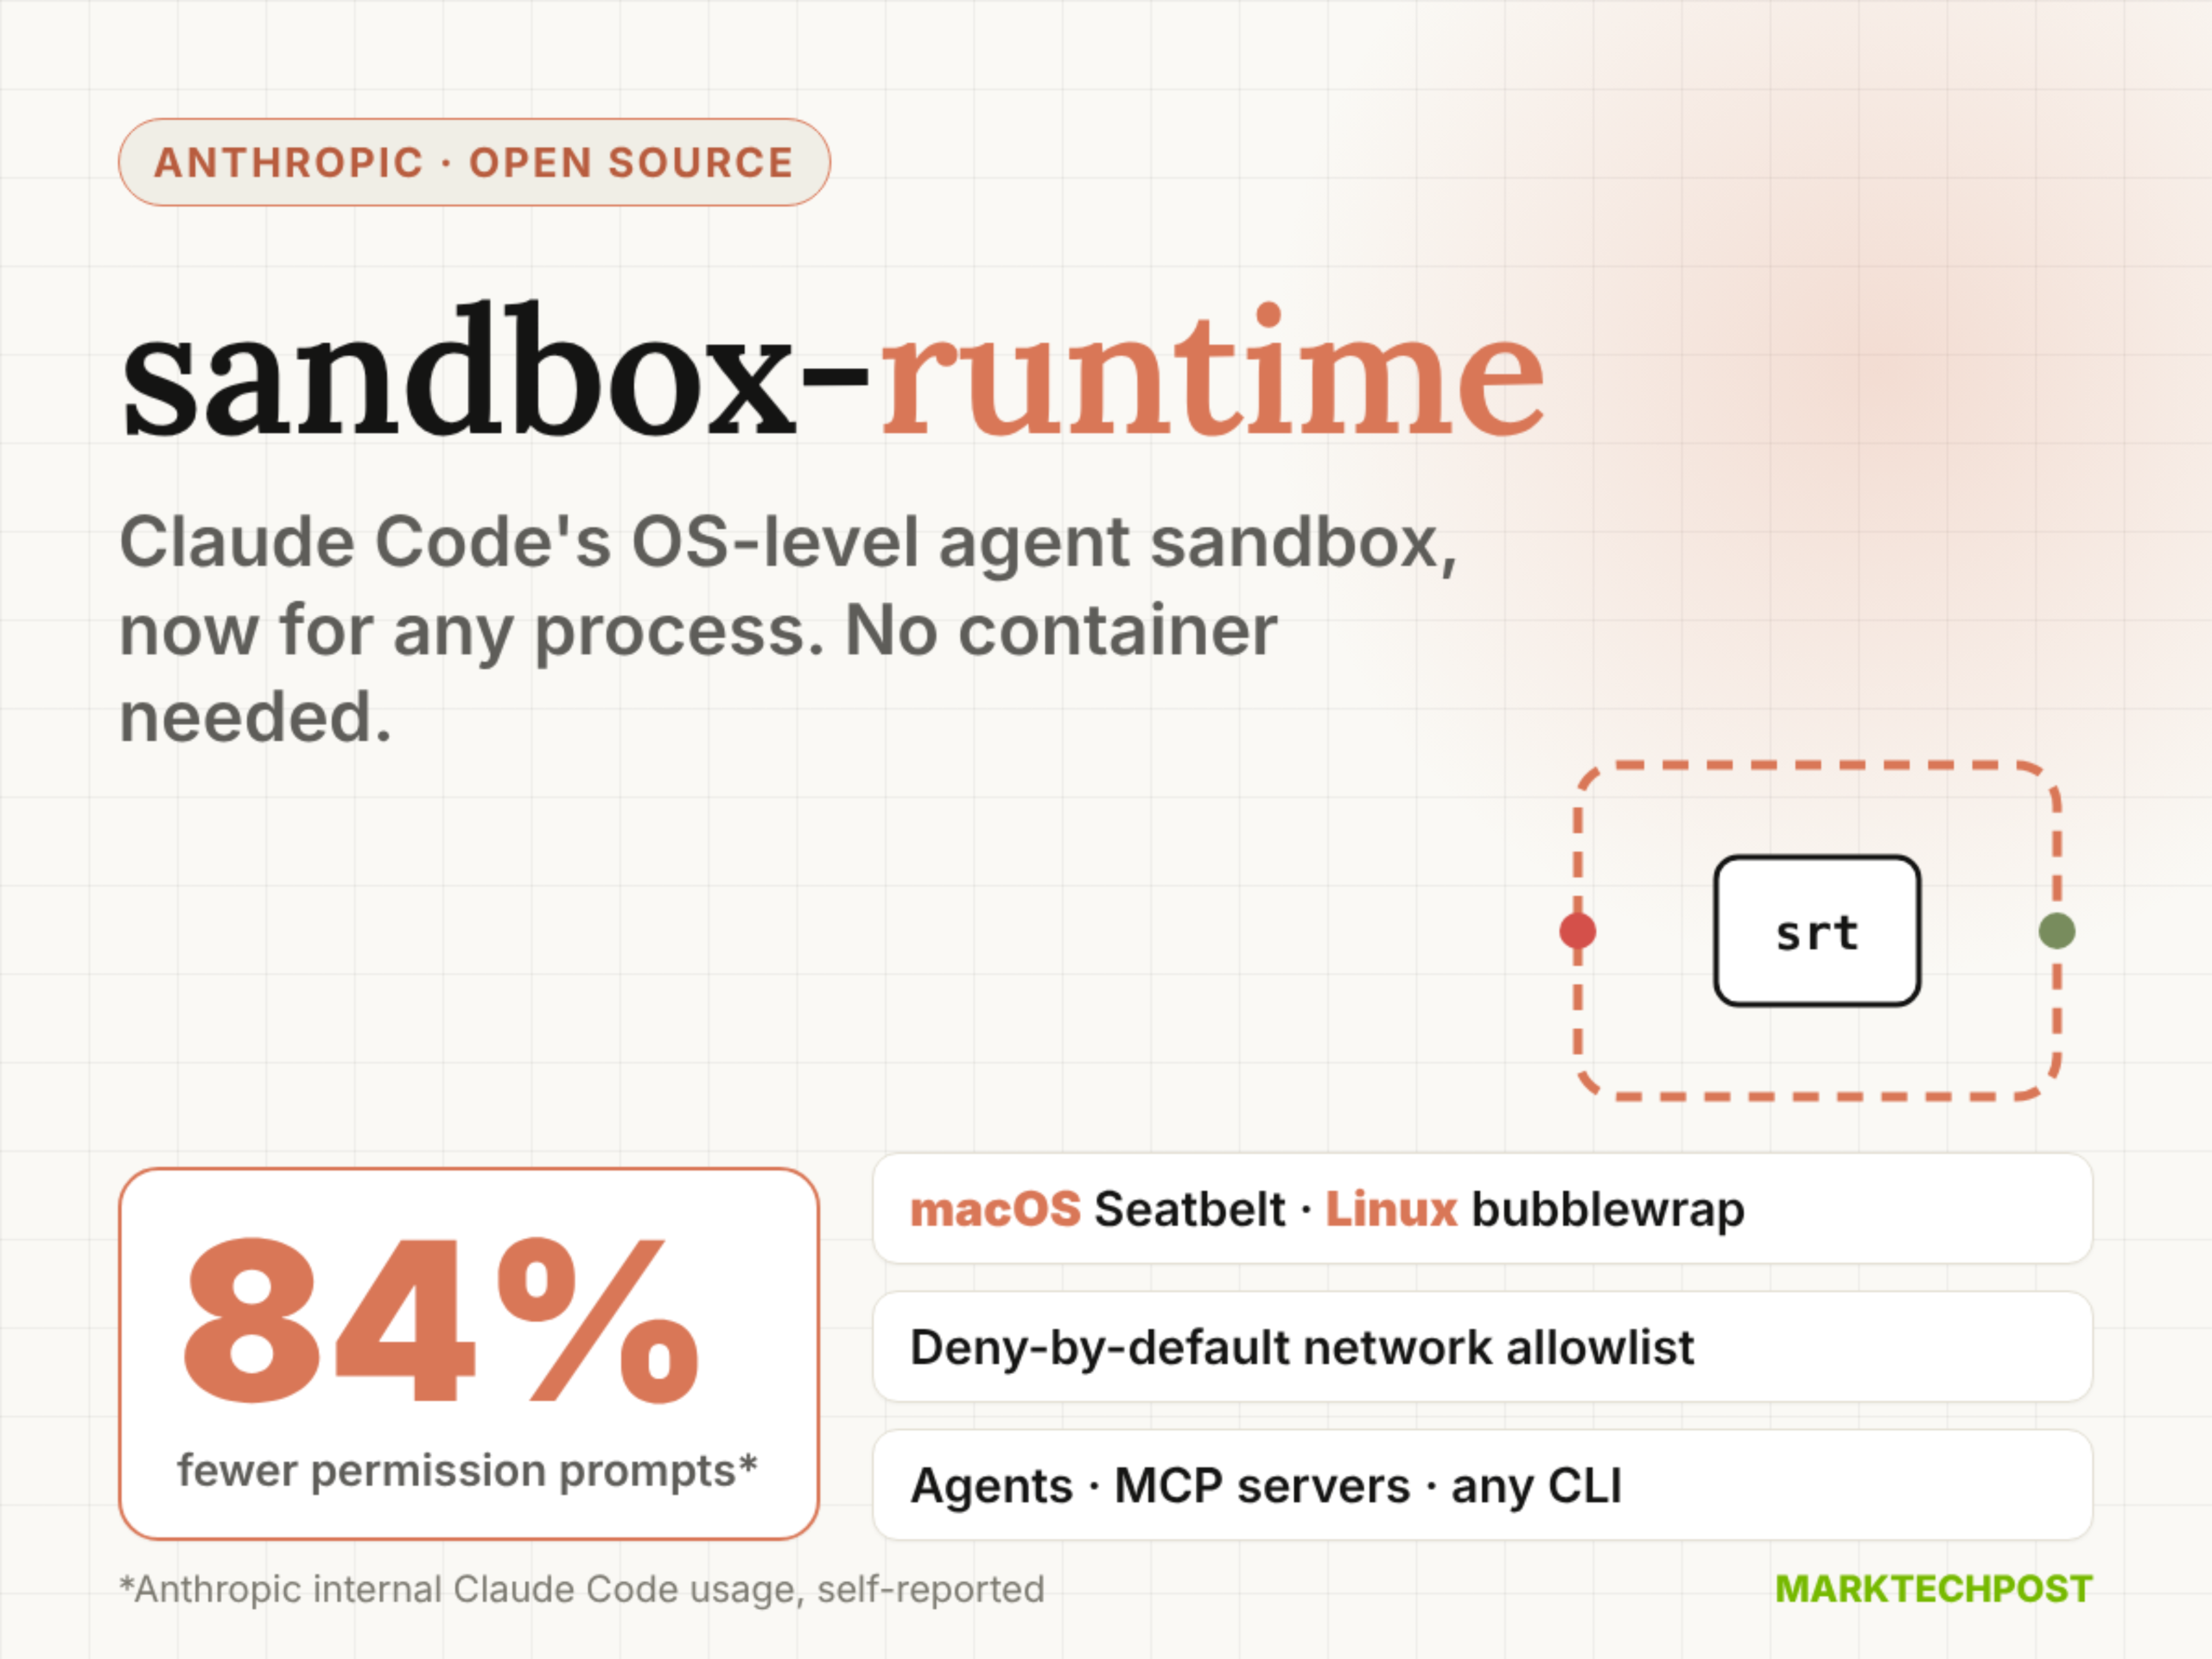
Anthropic open-sources the OS-level sandbox sandbox-runtime: providing container-free file and network isolation for AI agents.

On October 24, 2026, Anthropic open-sourced sandbox-runtime (srt), an OS-level sandboxing tool that operates without containers, designed to restrict file read/write and network access permissions for AI agents, MCP servers, and CLI tools. It supports macOS (Seatbelt), Linux (bubblewrap), and Windows (alpha), with npm package version 0.0.81 under the Apache-2.0 license.

Meet Anthropic’s sandbox-runtime: OS-Level Sandboxing for AI Agents, No Containers

Why it matters:This tool represents a significant advancement in AI security infrastructure—achieving fine-grained, full-process-tree coverage through the operating system’s native isolation mechanisms, directly addressing the risks of prompt injection and privilege escalation, and has already been deployed for internal validation within Claude Code.

Timeline and related coverage